Identity Providers
Configure the providers used for enterprise authentication.
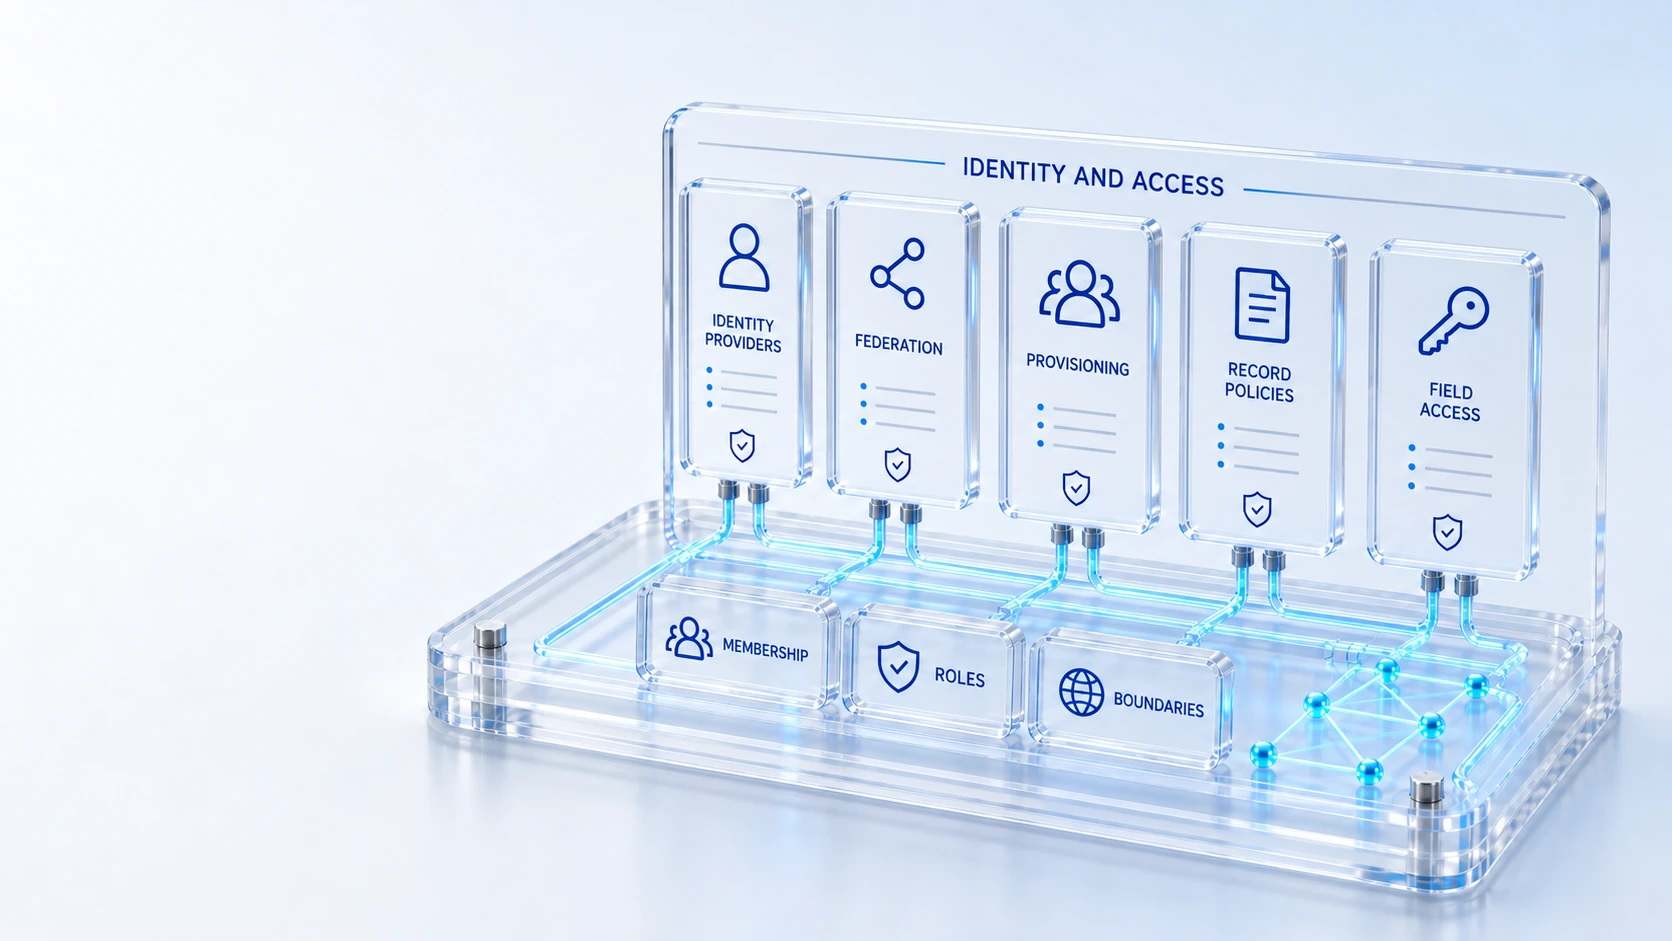
Identity ProvidersConfigure the providers used for enterprise authentication.
FederationConnect configured enterprise identity federation.
ProvisioningManage supported identity provisioning through platform administration.
Record PoliciesNarrow data access with configured record-level policies.
IdentityPolicy
Connect tenant identity, federation, provisioning and configurable record and field access to operational work.
Configure the providers used for enterprise authentication.
Connect configured enterprise identity federation.
Manage supported identity provisioning through platform administration.
Narrow data access with configured record-level policies.
Identity → Policy → Access
Explore the details below, then bring your workflow, source data and questions to a guided conversation.
Built into the platform
Configure the providers used for enterprise authentication.
Connect configured enterprise identity federation.
Manage supported identity provisioning through platform administration.
Narrow data access with configured record-level policies.
Apply configured field access within the authorized record context.
Respect access policy when traversing connected records.
Actual product view
See the running demo environment. Features and records are subject to your role, configuration and integrations.
Connected by design
Service records, configuration items, people, locations and evidence share the same operational foundation. Move from investigation to the related asset, service or customer workflow with clear ownership.
Explore the platform architectureImplementation context
Features depend on enabled modules, configured roles, source data and supported integrations. Agree your implementation scope and acceptance criteria during discovery.
Who this is for
A user’s ability to sign in does not establish which records or fields they should see. Enterprise access review must connect federation and provisioning with tenant identity, memberships and the configured policies governing related operational data.
Illustrative walkthrough
A fictional enterprise evaluates an employee, a customer contact and a vendor technician. The identity team inspects authentication and provisioning configuration, then checks permitted records, fields and relationship traversal for each representative operating responsibility. This is an illustrative evaluation scenario, not a claim about a customer deployment.
Review the configured identity provider, enterprise federation and supported provisioning context so the team understands how the representative user reaches the tenant. Configure the providers used for enterprise authentication.
Check the policies governing the selected operational record and its fields, identifying where configured access narrows what the signed-in role may inspect. Manage supported identity provisioning through platform administration.
Follow an allowed relationship and inspect the relevant case, portal or attachment context, verifying that related queries preserve the governing access policy. Apply configured field access within the authorized record context.
A credible access evaluation compares representative roles using the same operational example, showing both permitted information and a meaningful boundary at a record, field or connected relationship. Use demonstration records and preserve the applicable reporting scope.
Explore the platform
Open a workspace for a closer look.
Prepare the evaluation
These are evaluation criteria, not promised outcomes. Agree the baseline, scope, source coverage and acceptance method with the responsible owners before drawing conclusions.
Questions for this topic
No. Federation concerns the configured authentication path; tenant identity, role responsibilities and record or field policies still govern the operational information available to the user.
The platform’s relationship queries are designed to respect configured access policy, and evaluators should demonstrate the relevant traversal with representative roles and restricted records.
Supported identity provisioning must be configured through platform administration, and its actual behavior should be verified alongside the selected identity provider and organization membership model.
Your next operating chapter
Bring one workflow, one service challenge or one part of your estate. We’ll show you where Qintorava fits.